Guide · from Splunk
The Essential Guide to SIEM
Your security team faces significant challenges in today's threat landscape. They grapple with analyzing data noise and trying to gain visibility across hybrid, cloud and on-prem environments – all while being inundated
- Format
- Guide
- Published by
- Splunk
- Added
- 8 Jun 2026
About this guide
Your security team faces significant challenges in today's threat landscape. They grapple with analyzing data noise and trying to gain visibility across hybrid, cloud and on-prem environments – all while being inundated with vast amounts of data from various security and IT sources. It’s a struggle to address every minor security issue and prioritize major vulnerabilities before they escalate.
A market-leading security information and event management (SIEM) technology can solve these problems. Download The Essential Guide to SIEM to discover how a top-tier SIEM solution can help you:
- Make sense of data noise and enable fast action
- Detect accurately, streamline investigations and increase productivity
- Increase operational efficiency by unifying threat detection, investigation and response workflows
Listen or skim
Summaries are generated from this page’s text. Read the full piece for the detail.
More from Splunk
All 7 →
The Essential Guide to Continuous Asset and Identity Intelligence
The adage remains true: You can’t manage what you can’t see. Continuous asset and identity intelligence is a transformative approach to managing and securing the vast array of assets within an organization. In this
10 Essential Capabilities of the SOC of the Future
Security will never be simple. But with the right operating model, it can be manageable — and even proactive. That’s the promise of the SOC of the future.
The Essential Guide to Zero Trust
Now more than ever, organizations are turning to a zero trust strategy to secure their data and systems. Regardless of size or sector, zero trust is essential to any business in the wake of COVID-19. And high-profile
Elsewhere in Cybersecurity & Threat Management
See the category →
Cyber Threat Landscape Report 2026
Frontline intelligence on the cyber risks shaping ASEAN, Australasia, and East Asia.
F5 named an innovation, market, and product leader in KuppingerCole's GenAI Defense Leadership Compass
In their inaugural guide addressing the nascent and evolving space of AI security, KuppingerCole has released its Generative AI Defense Leadership Compass, naming F5 as an Innovation Leader. At F5, we are thrilled and
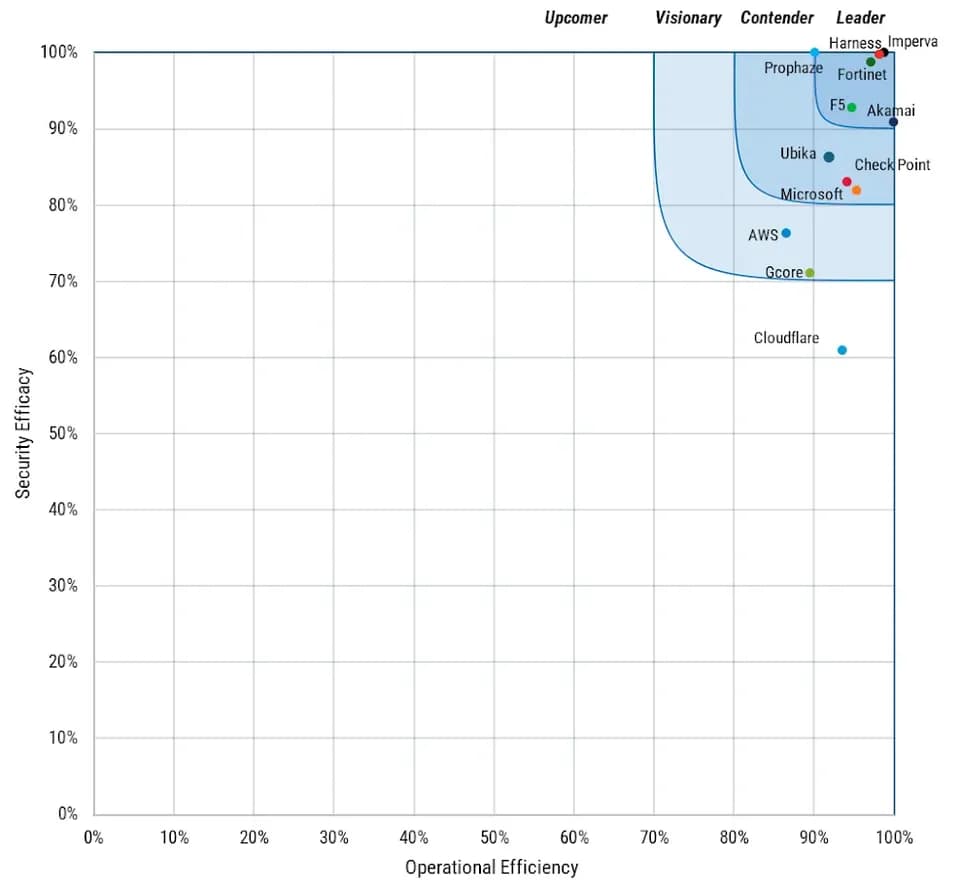
F5 named a leader in SecureIQLab’s Cloud WAAP v5.0 CyberRisk Validation Comparative Report
In SecureIQLab’s recent “Cloud WAAP v5.0 Comparative Report,” F5’s Distributed Cloud WAAP was placed in the Leader tier of the CyberRisk Ripple—the report's highest classification, reserved for solutions scoring well on